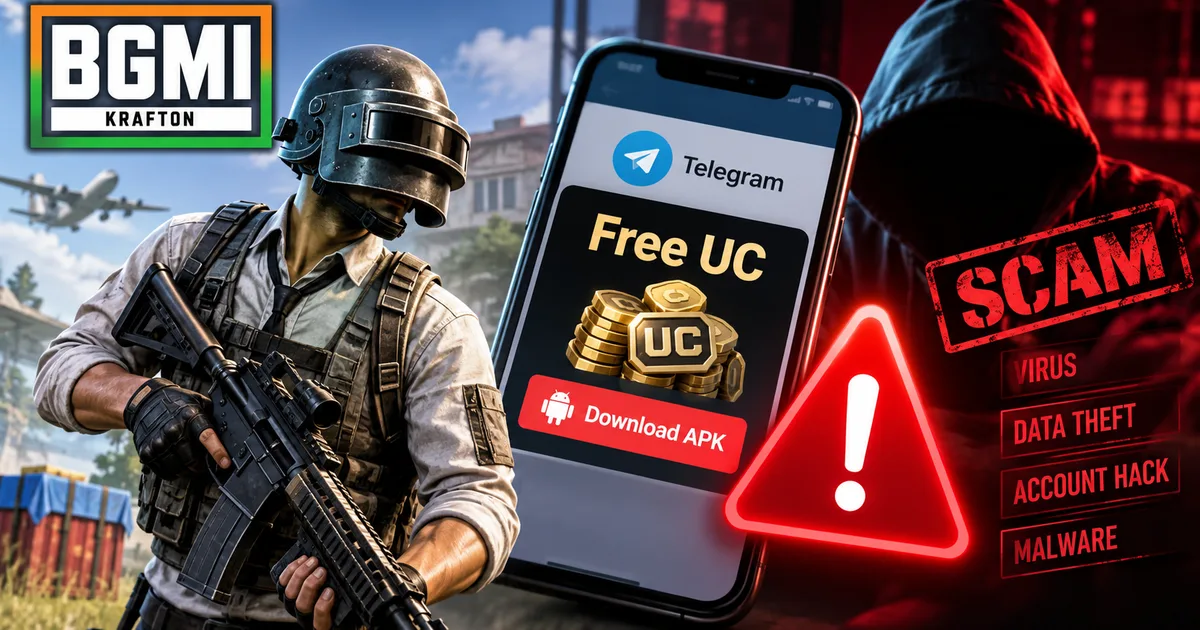
The hype for the new Battlegrounds Mobile India update is massive. Players want to try the new Evolving Universe theme mode and the Space Time Overlap mechanics in Erangel. But scammers are tracking this excitement. Right now, a fake BGMI September 2026 update free UC Telegram APK scam is destroying bank accounts across India.
I get it. You want to play the new update. Your friends are probably already exploring Pochinki with the Permanent Energy Bar and Automatic Recalls. You check the Google Play Store, and the update isn't there for your phone yet. So you open Telegram.
That's exactly what the fraudsters want you to do.
They know the official BGMI 4.3 APK download goes live around 12:30 PM IST on the official website. But they flood Telegram gaming groups hours earlier. They post links claiming to have the file ready. And to make the trap irresistible, they throw in promises of free in-game currency.
Honestly, in my experience, this is one of the most vicious gaming frauds I've seen this year.
What exactly is this Telegram APK scam
This fraud relies on impatience and greed. You're looking for the game update file. A message pops up in a Telegram channel with thousands of members. The message offers a direct download link for the BGMI 4.3 update.
It gets worse. The message also claims this specific APK file comes pre-loaded with free UC (which makes sense, actually, because people love free stuff). Sometimes they promise 5,000 UC. Sometimes it's 10,000 UC. They tell you it's a "modded" version or an "early access beta."
The file you download isn't Battlegrounds Mobile India. It's malware built to steal your financial data. The scammers disguise the icon to look exactly like the real game. Once installed, it quietly takes over your phone.
We saw something super similar recently with the Fake BGMI Lite 2026 Early Access APK Telegram Scam. Scammers recycle these tactics because they work. They just change the file name to match whatever game is currently trending.
People in India lose lakhs of rupees every month to these application frauds. The gaming community is a huge target. Younger players might not be as cautious about cybersecurity, especially when they think they're getting a good deal on expensive in-game items.
How the fraud actually works step by step
Understanding how this attack works is your best defense. The criminals run this operation like a well-oiled machine.
Step 1: The bait drops in Telegram groups
Fraudsters create fake Telegram channels that look like official BGMI community groups. They use stolen logos and post legitimate game news to build trust. Then they drop the bait message. It usually includes a fake screenshot showing an account with massive amounts of UC. The text urges you to download quickly before the link expires. They create a sense of artificial urgency.
Step 2: You download the malicious file
You click the link and download an APK file. An APK is just an Android application package. The file name usually looks legitimate, something like "BGMI_4.3_FreeUC_Update.apk". Your Android phone will warn you about installing apps from unknown sources. But the scammers include instructions telling you to ignore this warning and allow the installation. They tell you it's completely safe and just a standard developer warning.
Step 3: The permission trap
This is where the real damage happens. You open the fake app. It doesn't launch a game. Instead, it asks for a bunch of permissions. The most critical one is SMS access. The app claims it needs to read your messages for "account verification" or "anti-cheat checks."
Never give SMS permissions to a game. The moment you hit allow, the malware starts forwarding all your incoming text messages to a server controlled by the scammers. The app screen might just show a fake loading bar that never finishes. It keeps you distracted while the background process goes to work.
Step 4: The financial drain
Now the criminals have full access to your SMS inbox. They go to banking apps or UPI platforms and initiate a login using your phone number. When your bank sends an OTP, the malware intercepts it. The scammers enter the OTP, log into your account, and drain your money.
They'll transfer funds from your SBI, HDFC, or ICICI accounts. They'll max out your linked credit cards. You won't even know it's happening because the malware often hides the incoming SMS notifications from your bank. You only find out hours later when a transaction fails or you check your balance on another device. I'm not sure exactly why banks haven't found a workaround for this yet.
Why this specific update is causing so much chaos
The criminals timed this attack perfectly. The new update brings the Evolving Universe mode, which completely changes how the game is played on Erangel. People want to try the new Permanent Energy Bar and the Automatic Recalls. Nobody wants to be the only person in their squad stuck playing the old version.
Plus, there are always rumors about new glacier skins or mythic outfits. Players think if they download an early APK, they might get a head start on unlocking them. Scammers exploit this FOMO. They know you're refreshing the Play Store, getting frustrated, and looking for alternatives.
Basically, you have to stay disciplined. The official website clearly states that the APK download goes live around 12:30 PM IST. Any file circulating before that exact time is guaranteed malware. And even after that time, you should only click the link on the official Krafton domain.
The official BGMI application doesn't require you to disable your phone's security protocols. If an installation guide tells you to ignore Google Play Protect warnings, you're installing a virus. Period.
Red flags you should never ignore
You can spot these scams easily if you know what to look for. Here are the biggest warning signs.
- Offers of free UC. Krafton doesn't give away thousands of UC for free in random Telegram updates. UC costs real money. If someone offers it for free, it's a scam. There are no secret cheat codes or modded versions that bypass the payment system.
- The source is not official. The only safe places to get the game are the Google Play Store, the Apple App Store, and the official battlegroundsmobileindia.com website. If the file comes from a generic file-hosting site or a direct Telegram upload, it's sketchy.
- Tiny file sizes. The real BGMI update is huge, often over 1GB. Fake APKs are usually tiny, around 10MB to 50MB. They only contain the malware payload and some basic graphics.
- Strange permission requests. A battle royale game needs microphone access for voice chat and storage access for game files. It absolutely doesn't need to read your SMS messages or manage your phone calls.
If you regularly download files from messaging apps, you should check out our broader Scam Alerts & Safety section. We track these threats daily. Just last week, we exposed the Fake Mirzapur Movie 2026 Telegram Download APK Scam. It used the exact same SMS interception trick on movie fans.
How to protect your phone and your bank account
Staying safe requires changing a few habits. You need to lock down your device and stop trusting random links.
First, never sideload apps from Telegram or WhatsApp. I can't stress this enough. Turn off "Install from unknown sources" in your Android settings. Go to Settings, then Security, and make sure this option is disabled. Only turn it on temporarily if you're downloading the APK directly from the official Krafton website. Then turn it off right after the installation finishes.
Second, audit your app permissions right now. Go to your phone settings, navigate to privacy, and look at which apps have access to your SMS. If you see a game or a weird flashlight app with SMS access, revoke it immediately. You should also check which apps have access to your accessibility services, as malware often abuses those to read your screen.
Third, rely on official channels. If the update is delayed on the Play Store, just wait. A few hours of waiting is better than losing your entire month's salary to a cybercriminal in Jamtara. You can always read the Latest Tech News to find out when the official rollout reaches 100% of users across all Android devices.
Look, you have to be skeptical of gaming community links. Scammers frequently buy old Telegram channels with thousands of subscribers. A channel might seem trustworthy because it has 50,000 members, but that means nothing. The original owner probably sold the channel to fraudsters. Now they use the established audience to push malware.
What to do if you already downloaded the fake file
If you realize you installed the fake APK, you need to act fast. Don't wait to see what happens. Every second counts when criminals have access to your OTPs.
Turn on airplane mode immediately. This cuts off the internet connection and stops the malware from sending your OTPs to the scammers' server. It isolates your phone from the network.
Go to your app settings and uninstall the fake application. Sometimes malware hides its icon to make this difficult (annoying, I know). If you can't find it, go to Settings, then Apps, and look for any app with a blank icon or a name you don't recognize. Uninstall it from there. Then reboot your phone.
If you gave the app SMS permissions, you should assume your banking details are compromised. Call your bank immediately. Use another phone if you have to. Tell them to block your UPI ID and freeze your net banking access. They handle these requests every day and will secure your account.
You should also change the passwords for your email accounts and social media profiles. If the malware had access to your device, it might have scraped saved passwords or session tokens.
Where to report this cybercrime in India
You must report these incidents. Even if you caught it in time and didn't lose money, reporting helps authorities take down the scammer's infrastructure and track the money mules they use to funnel the stolen funds.
File a formal complaint on the National Cyber Crime Reporting Portal at cybercrime.gov.in. The process is straightforward and you can do it entirely online without visiting a police station. Just provide all the details, including the Telegram group name and the link you clicked.
If money has already been deducted from your account, call the national cybercrime helpline at 1930 immediately. Call them before you call your bank, or right after. The 1930 helpline can sometimes freeze the fraudulent transaction and recover your money if you report it within the first "golden hour" after the theft occurs.
The Indian Computer Emergency Response Team (CERT-In) regularly warns about these types of malware campaigns. They track how these syndicates operate across borders. These aren't kids playing pranks. They're organized criminal networks stealing crores of rupees every week from unsuspecting internet users.
Protecting yourself means being patient. Wait for the official update on the Play Store. A rush for new features just isn't worth losing your hard-earned savings over.